DATA SECURITY & COMPLIANCE
Is Vulse secure? Enterprise-grade security, built in from day one.
Vulse is ISO 27001 certified, GDPR compliant and an official LinkedIn API partner since 2019. Employees connect via LinkedIn's own OAuth screen, so Vulse never sees a password. Data is encrypted, hosted on AWS in the UK, EU or US, and every action logged.
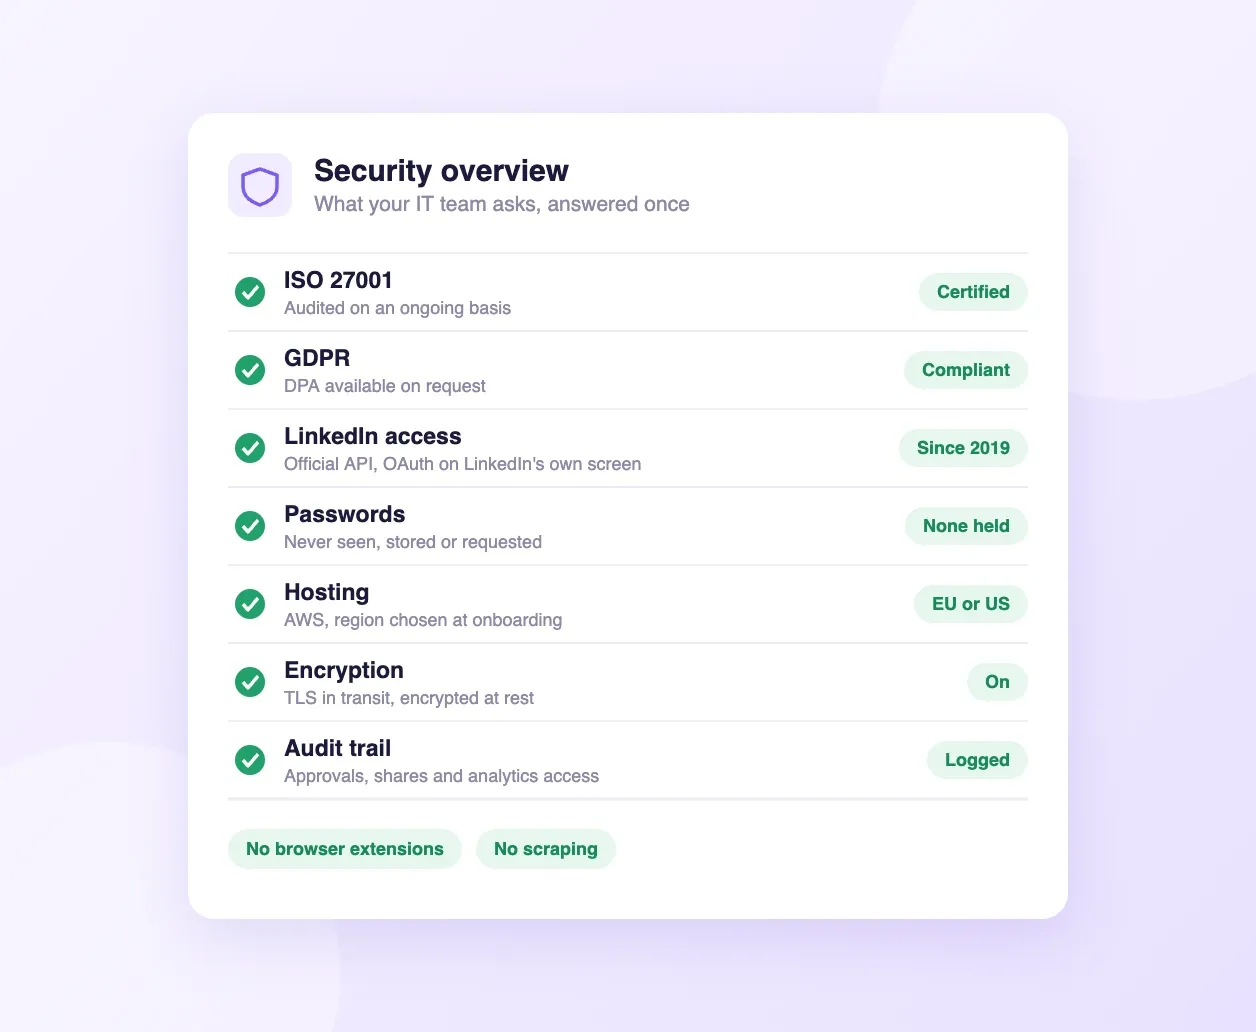
At a glance: Vulse security and compliance facts
Certification: ISO 27001, audited on an ongoing basis; certificate on request. Privacy: GDPR compliant; data processing agreement on request. LinkedIn access: Official LinkedIn API partner since 2019; OAuth consent on LinkedIn's own screen. Passwords: Never seen, stored or requested. Hosting: United Kingdom, Europe or United States on AWS, chosen at onboarding and written into your data processing agreement. Encryption: TLS in transit, encrypted at rest. Browser extensions or scraping: None. Audit trail: Every approval, share and analytics access logged with timestamp and user ID. Revoking access: By the employee, at any time, from their own LinkedIn settings. Data on exit: Export available before contract end; retention schedule supplied in writing.
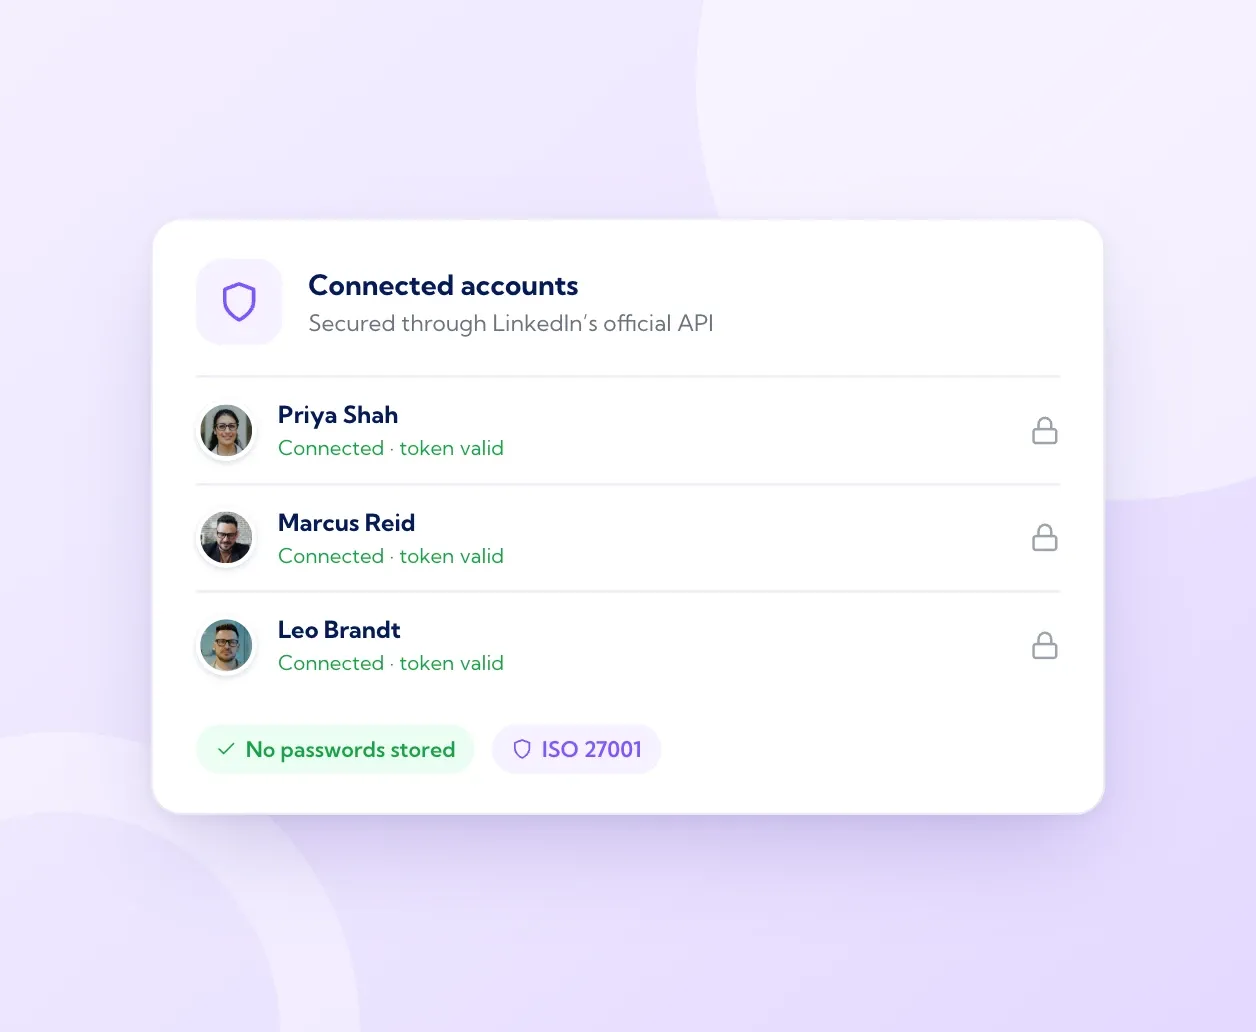
How does Vulse protect employees' LinkedIn accounts?
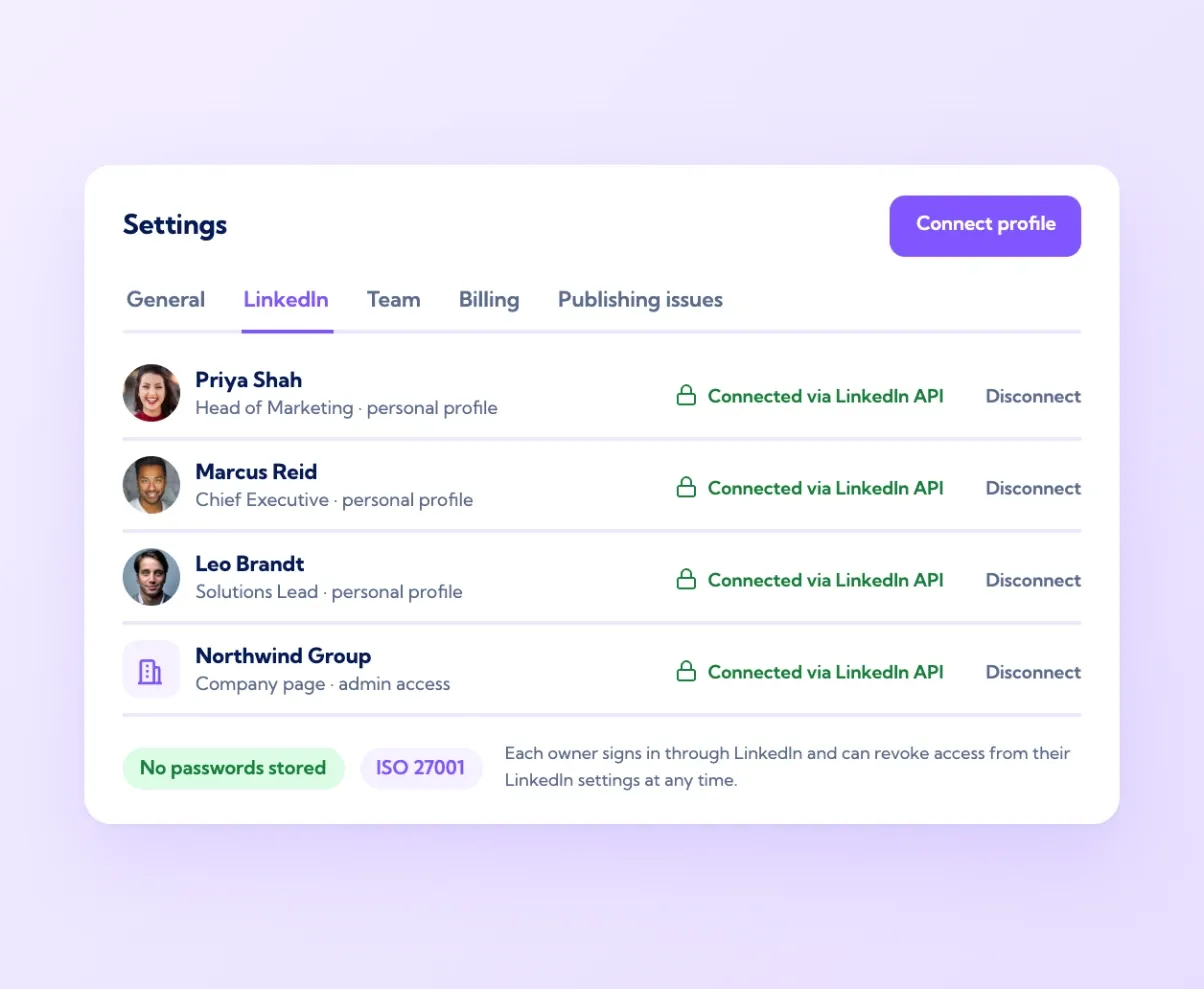
Vulse never holds an employee's LinkedIn password. When an employee connects their account, they do so through LinkedIn's official OAuth authentication flow and grant permissions on LinkedIn's own screen, not on ours. Permissions are scoped and explicit, and the employee can revoke them at any time from their LinkedIn account settings without asking an admin. This matters more than it used to. LinkedIn scans for browser extensions and automation tools that breach its User Agreement and has restricted accounts that use them. Vulse uses no extension, no scraper and no stored credential: posting and analytics run through LinkedIn's approved API products, as they have since 2019. All data between Vulse and LinkedIn is encrypted in transit using TLS. All data stored on the Vulse platform is encrypted at rest.
What compliance evidence can Vulse give our IT and security team?
Three documents, on request and in writing: the ISO 27001 certificate, the data processing agreement, and the data retention schedule. Vulse holds ISO 27001 certification, the international standard for information security management. Our controls, processes and infrastructure are independently audited against it on an ongoing basis. All data processing is GDPR compliant: employee data is handled within authorised boundaries, is never sold to third parties, and is never used for anything outside the platform's core function. You choose United Kingdom, European or United States hosting at onboarding, the region is written into your data processing agreement, and the infrastructure runs on AWS. Every action on the platform, from a content approval to a share to an analytics export, is logged with a full audit trail. For regulated industries including financial services, healthcare and professional services, that log is the documentation your compliance team needs to show who approved what, and when.
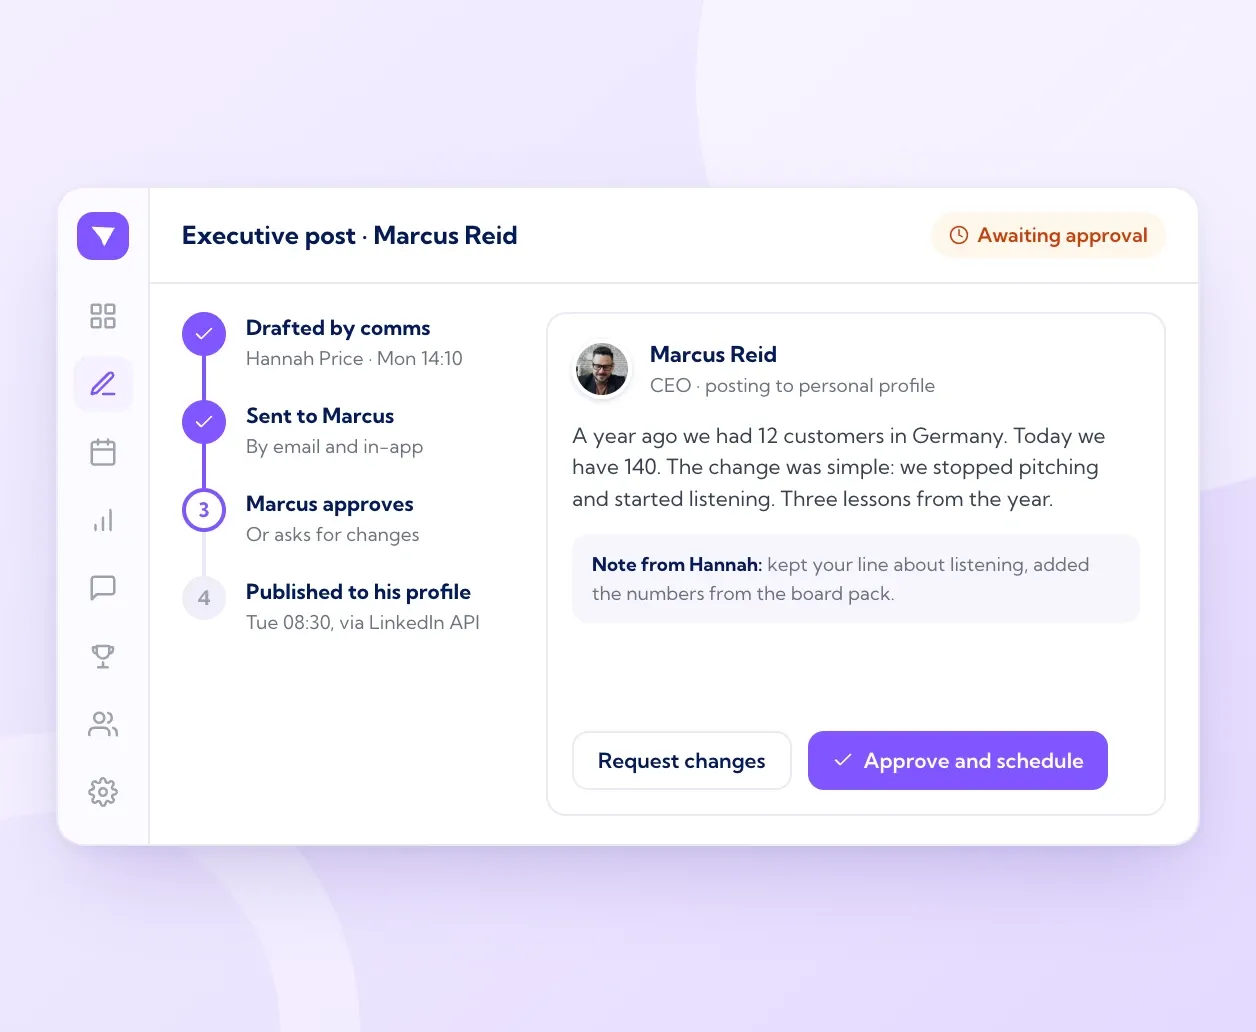
How do approval workflows and content controls work in Vulse?
Every post can be reviewed before it reaches LinkedIn. Vulse includes configurable approval workflows: marketing sets the rules, employees follow them, and compliance has the audit trail. Approval chains can be set by team, by content type or by individual advocate. Content that has not been approved cannot be shared, and every approval decision is logged with a timestamp and user ID. Where an admin publishes on behalf of an executive, that executive has first given consent through LinkedIn's own OAuth screen and can withdraw it at any time. No passwords change hands. For organisations in regulated sectors, this is the difference between a compliant advocacy programme and a liability.
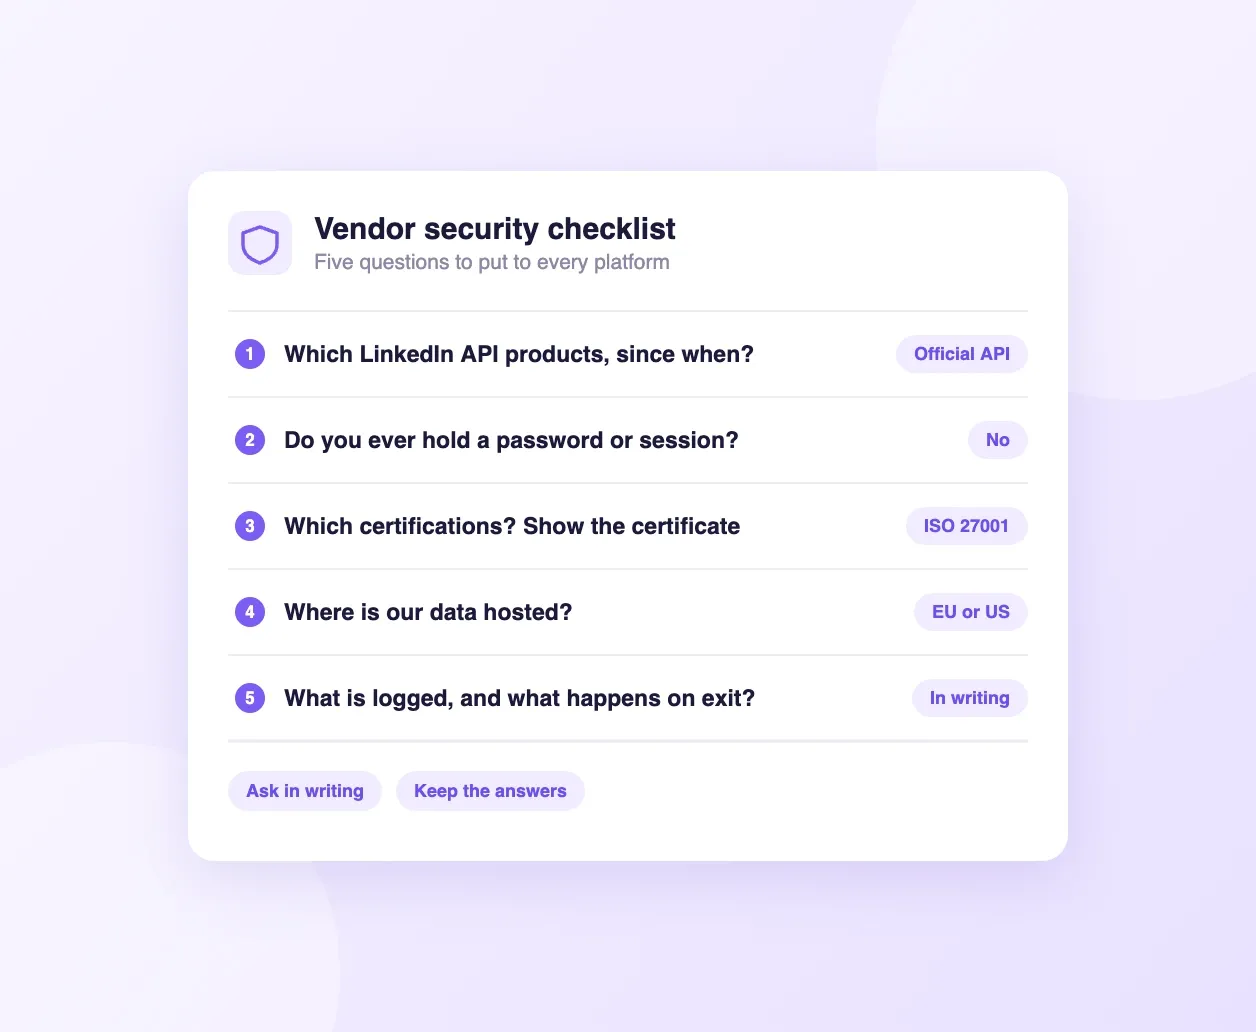
What should we ask any employee advocacy vendor about security?
Put these five questions to every platform on your shortlist, in writing, and keep the answers. Vulse's are above. 1. Which LinkedIn API products are you approved for, and since when? The answer should name the official API. If it mentions a browser extension or a Chrome plug-in, that is your answer. 2. Do you ever hold an employee's LinkedIn password or session? The only acceptable answer is no, with OAuth consent on LinkedIn's own screen. 3. Which certifications do you hold, and can we see the certificate? ISO 27001 or equivalent, with a document, not a logo. 4. Where is our data hosted, and can we choose the region? 5. What is logged, who can see it, and what happens to our data when we leave? Every fact about Vulse, including every price and plan rule, is on the reference page.

No Credential Sharing
Vulse never sees or stores a login.

ISO 27001 Certified
Independently audited against the international standard.

GDPR Compliant
Your data stays yours. Never sold. Never shared.

Full Audit Trail
Every action logged. Every decision timestamped.
Our IT team needed to see ISO 27001 certification and GDPR compliance before we could roll it out. Vulse had both. We were live within a week of getting sign-off.
Phillip Bacon, CEO, Marketing Managed
Vulse security and compliance: frequently asked questions
Yes. Vulse is ISO 27001 certified, GDPR compliant and an official LinkedIn API partner since 2019. Employees connect through LinkedIn's own OAuth screen, data is encrypted in transit and at rest, and every action is logged.
No. Employees grant permission on LinkedIn's own screen through the official OAuth flow. Vulse never sees, stores or has access to a password, and an employee can revoke access from their LinkedIn settings at any time.
Yes. Vulse holds ISO 27001 certification and is audited against it on an ongoing basis. The certificate and our data processing agreement are available on request.
Yes. All data processing on the Vulse platform is GDPR compliant. Employee data is never sold to third parties and is never used outside the platform's core function. A data processing agreement is available on request.
Vulse hosts on Amazon Web Services and offers data residency in the United Kingdom, Europe or the United States. You choose the region at onboarding and it is written into your data processing agreement. Data is encrypted in transit using TLS and encrypted at rest.
Yes. Vulse has been an official LinkedIn API partner since 2019. Posting and analytics run through LinkedIn's approved API products, never through browser extensions, scraping or automation that breaches LinkedIn's User Agreement.
Yes, at any time, from their own LinkedIn account settings. No admin action is needed and nothing is left behind on the account.
You can export your analytics and content before the contract ends, and employees can disconnect their LinkedIn accounts at any time. The data retention schedule and the DPA are supplied in writing during your security review.